Know who authorized every system you run.
Prove it when asked.

The authorization layer for automated systems

The signed record of who accepted the risk, what the system may do, and until when.

The agent removed
40,000 posts.

Who said it could?

authorization0 results
#Slack—
Email—
Jira—
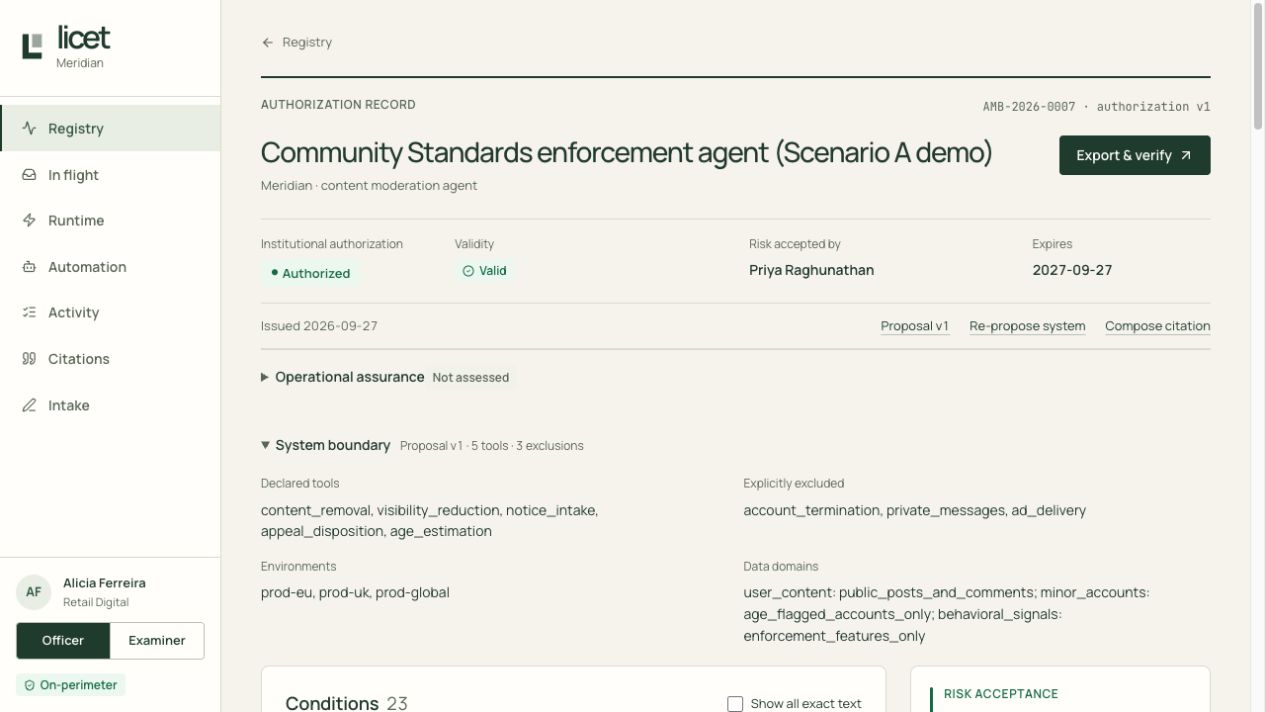
Authorization recordAMB-2026-0007 · authorization v1

Community Standards enforcement agent

Meridian · content moderation agent

Institutional authorization
Authorized
Validity
⊙ Valid
Risk accepted by
Priya Raghunathan
Expires
Issued
Operational assuranceIndependent evaluation · attached
Illustrative attachment · fictional sample

Independent evaluation — example attachment

This sample demonstrates where an evaluation attachment would appear in the record. No evaluation was performed for this illustration. It contains no evaluator, findings, test results, or assurance opinion and is not part of the signed public demonstration record.
System boundaryProposal v1 · 5 tools · 3 exclusions
Declared tools
content_removal, visibility_reduction, notice_intake, appeal_disposition, age_estimation
Explicitly excluded
account_termination, private_messages, ad_delivery
Environments
prod-eu, prod-uk, prod-global
Data domains
user_content: public_posts_and_comments; minor_accounts: age_flagged_accounts_only; behavioral_signals: enforcement_features_only
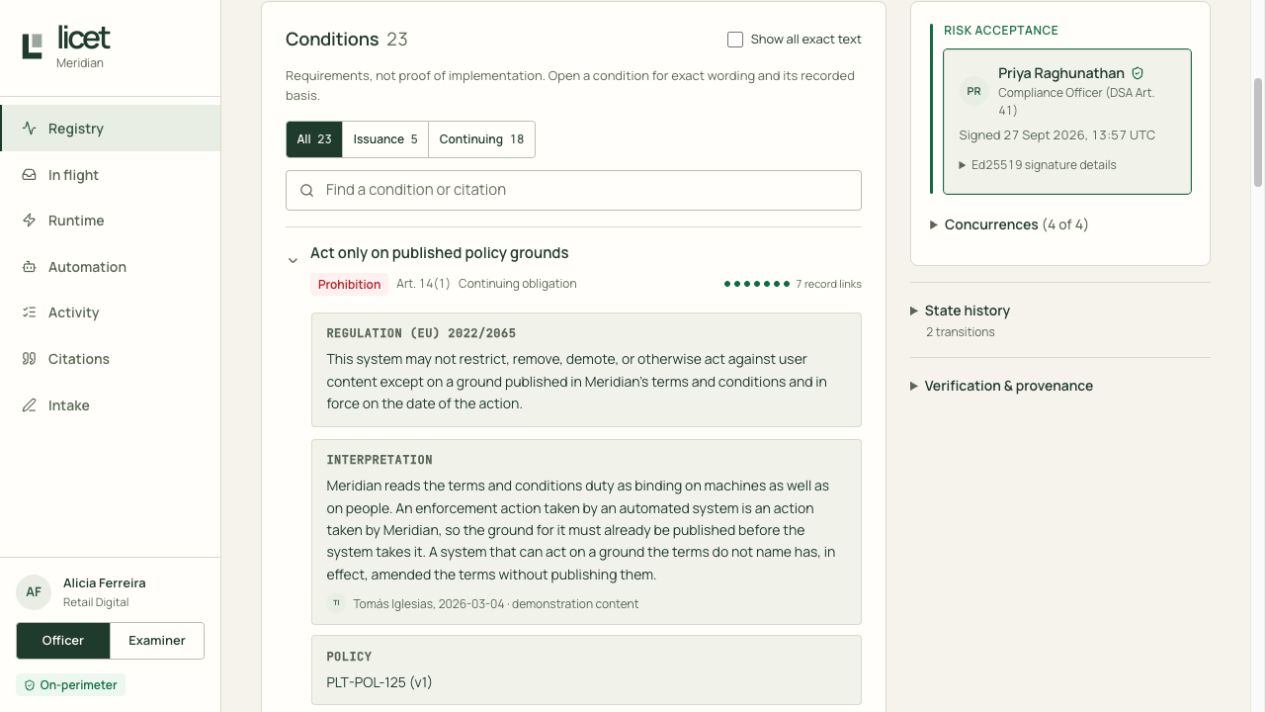
Conditions 23
Act only on published policy grounds
Risk acceptance
Priya Raghunathan
Illustrative demo state · Fictional institution and reviewers · Evaluation attachment is a sample

One record.
One accountable name.

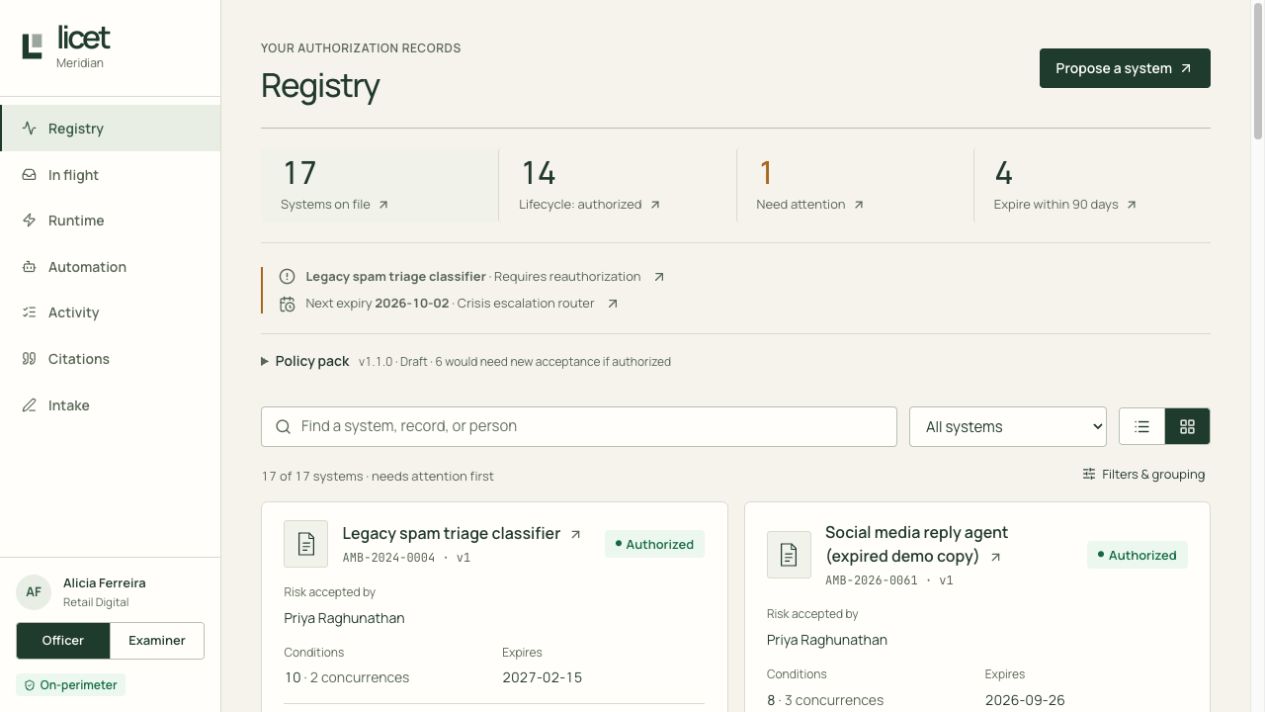
For platform teams

Make the boundaries of automation explicit. See what has been authorized, which conditions apply, and where permission ends.

Actual licet Registry showing demonstration system records and authorization status.

For legal & policy teams

Keep institutional decisions connected to their sources, interpretations, and owners. Produce the record when someone asks.

Actual licet condition showing a source, attributed interpretation and policy reference.

From institutional decision
to lasting record.

Bring scope, conditions, exclusions, and the named risk acceptor together in a signed, versioned record.

Inspect a signed demonstration record ↗

Optional runtime enforcement. Check proposed actions against the recorded authorization before they proceed. Production executor integration is required.

The actual licet authorization record with its system boundary expanded.
The scope and exclusions remain attached to the institutional decision.

Built by the people who had to sign off.

About licet ↗
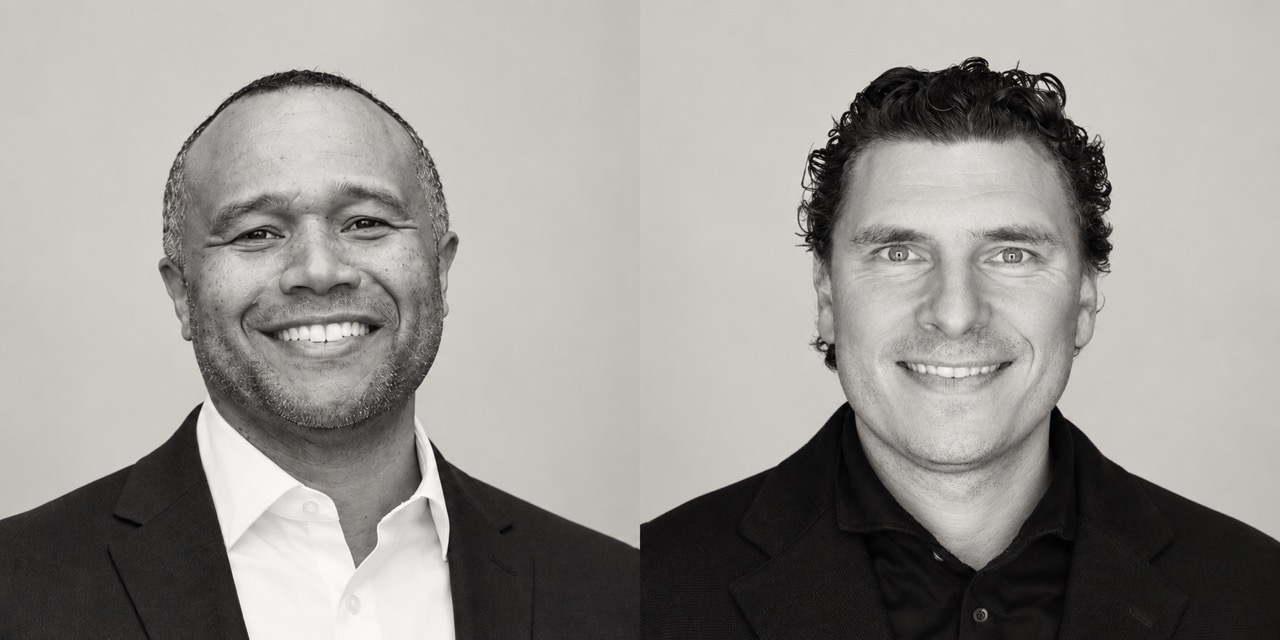
David Gleaton, co-founder and CEO of licet.

David Gleaton

Co-founder & CEO

Twenty years across seven federal agencies, where no system goes live until a named official accepts its risk in writing. licet brings that discipline to every automated system. American Service Fellow in the Mid-Career MPA program at Harvard Kennedy School. MA in Strategic Studies, Air War College.

David’s story at Harvard Kennedy School ↗
Dimitri Morarcaliev, co-founder of licet.

Dimitri Morarcaliev

Co-founder

Swiss lawyer and former compliance lead for a Swiss cantonal government. MC/MPA candidate at Harvard Kennedy School, selected as Switzerland’s representative on a Harvard sovereign AI project.

Patent
pending
The record is the product

Evidence you
can inspect.

Preserve the institution’s decision in a form that product, policy, legal, and independent reviewers can examine.

Read the signed demonstration record ↗

An authorization record documents institutional permission.

Named approvals

Keep the risk acceptance and concurrences attached to the version that was approved.

Conditions with context

Preserve the sources, interpretations, limits, and evidence requirements behind the decision.

Independent record verification

Checking signatures…
MER-2026-0001 · Ed25519
Risk acceptance key · SHA-256
Checking public key…
All four approval keys
Demo keys · Embedded MER-2026-0001 record · Signature integrity
Demo snapshot & limits
Signed record
MER-2026-0001
Contents
13 recorded conditions · 4 demo approvals
Fictional risk acceptor
Priya Raghunathan · Compliance Officer (DSA Art. 41)
Recorded expiry
14 MAR 2027

Demonstration signatures establish no real-world identity or approval. Operational assurance is not assessed; legal compliance is not determined. This is a fixed snapshot, not a current authorization check.

Start with one consequential workflow.

Design partners

Now selecting design partners.

BECOME A DESIGN PARTNER

Start with one system.

Tell us what you run and the question you need to answer.

Only pressing Submit sends your details. We save your introduction and use it to respond; unfinished entries are not collected. Please keep it nonconfidential. Privacy